After implementing the most recent iFix, following best practices for your IBM ELM environment, have you encountered an issue where your widgets are no longer functioning, and you are unable to identify the root cause of the problem?
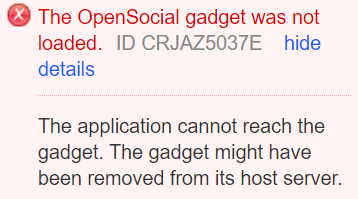
01 / 03Problem of CRJAZ5037E SSRF:
The introduction of new iFixes, starting with versions ELM 7.0.2 iFix004, ELM 7.0.1 iFix009, CLM 6.0.6.1 iFix018, and CLM 6.0.6 iFix022, underscores IBM’s commitment to bolstering security. This initiative addresses Server-Side Request Forgery (SSRF) vulnerabilities.
Consequently, due to these implemented security measures, there are notable changes in the behavior of all OpenSocial gadgets and RSS feeds that fetch content from external sources. This adjustment becomes apparent through errors encountered while attempting to integrate widgets into your side-panel or dashboard, particularly those that previously operated seamlessly.
02 / 03Solution for CRJAZ5037E SSRF:
To effectively address this issue and reinstate the functionality of your widgets, it is imperative to incorporate the URLs of your extension hosting servers into the jazz “allowlist.” Access the allowlist via the JTS application (https://yourServer/jts/admin) in the Admin menu. Proceed to “Advanced properties,” where you can locate the “allowlist.” Within this section, diligently input all URLs linked to your hosting servers, ensuring they are separated by commas and devoid of spaces. As an alternative, consider utilizing an asterisk “*” to grant permission for all traffic, a practical approach if deemed appropriate.
Subsequent to the mentioned step, it is crucial to include the requisite URLs in the whitelist of the CLM/ELM application you are integrating your widgets with. For example, if your aim is to integrate widgets into RM applications, navigate to https://yourServer/rm/admin. In the side-menu, specifically find and select “Whitelist,” then proceed to systematically incorporate the necessary URLs into this designated section.
More information about: CRJAZ5037E Changes to Engineering Lifecycle Management related to Server-Side Request Forgery (SSRF) vulnerabilities.
 Enlarge
 Enlarge
 Enlarge
03 / 03Exact settings and how to verify
Affected versions
IBM’s technote ties the change to ELM 7.0.2 iFix004, ELM 7.0.1 iFix009, CLM 6.0.6.1 iFix018 and CLM 6.0.6 iFix022. The technote is filed against 7.0.1, 7.0.2 “and future releases”. It affects OpenSocial gadgets and RSS feeds that fetch content from an external service. The full technote text requires an IBM login.
Where the settings are
- Jazz Team Server: open
https://<server>/jts/admin, go to Server > Advanced Properties and search for the servicecom.ibm.team.repository.service.opensocial.gadgetprovider.OpenSocialGadgetProviderRestService. In the property “List of allowed external resources”, enter the URL of each server that hosts your widgets. - Application that shows the widget (for example
https://<server>/rm/adminfor DOORS Next): in the Communication section, open Allowlist (Outbound) and add the widget host as a base URL in the formscheme://domain:port/.
IBM made this change to reduce SSRF risk by allowing communication only with sites that are explicitly listed. Listing your actual widget hosts keeps that protection in place.
How to verify
- Open the gadget XML URL in a browser. It should render or download without errors.
- In IBM’s own widget setup procedure, the last step is a Jazz Team Server restart. Plan for one if the change does not take effect straight away.
- Reload the dashboard or mini dashboard and check that the widget loads without CRJAZ5037E.
Sources: IBM technote on SSRF changes, Managing the URL allowlist (ELM 7.1), Configuring DOORS Next for a widget (IBM Engineering AI Hub).
Need help with IBM ELM?
We plan, implement and support IBM Engineering tools for regulated teams.
Book a free 30-min consultationTools, training and help for IBM ELM widgets
The tools from this post, and how we help your team put them to work.




 IBM ELM